Server Setup & Configuration

Server setup -- a new server, ready in 4 hours, not 4 weeks.

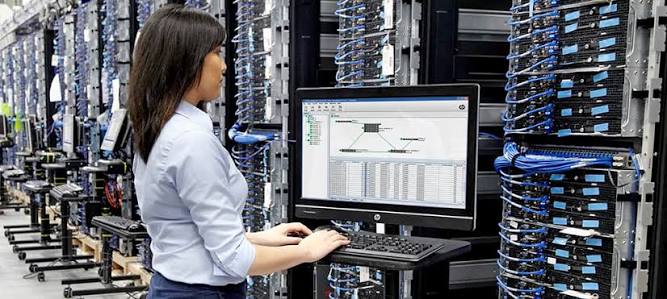
We provision your new server end-to-end: OS install, network config, security baseline, web stack, database, backups, monitoring, firewall. You give us root, we hand you a production-ready box. Same checklist every time, no skipped steps.
⚡ 4-hour turnaround
🛡️ 150-point checklist
How we do it

A 6-step process. Every server, every time.

01

Receive access

You share root credentials via 1Password or Bitwarden. We change the root password and rotate SSH keys. Access logged in our audit system.

15 min
02

Audit current state

We snapshot the current state, run a 150-point health check, identify risks. Documented in a report. We do not skip this step even if the server looks clean.

45 min
03

Network + DNS

Hostname, /etc/hosts, rDNS, IPv6, firewall rules, SSH port (non-default), fail2ban, MFA. All locked down before we install anything else.

30 min
04

Web stack

Install your choice: nginx, Apache, OpenLiteSpeed, LiteSpeed. PHP versions you need, MySQL/PostgreSQL, Redis, Varnish. All tuned for your workload.

90 min
05

Backups + monitoring

Offsite backups scheduled. Monitoring agents installed. Alert routing configured. Runbooks written for common issues. Smoke tests passed.

60 min
06

Hardening report

You get a 12-page PDF with everything we did. Every change, every decision, every password rotated. Plus 30 days of free support to fix anything.

20 min
The full checklist

What is on the 150-point checklist?

28

OS & Kernel

  • Latest stable kernel (or LTS for stability)
  • sysctl hardening (30+ parameters)
  • Disable unused modules (bluetooth, firewire, etc.)
  • Kernel live-patching (Livepatch or Ksplice)
  • Filesystem tuning (noatime, xattr)
  • Time sync (chrony with NTP pool)
  • Locale, timezone, hostname
  • Updates repo pinned and tested
32

Network & Firewall

  • Default-deny iptables/nftables rules
  • Non-standard SSH port (random from 1024-65535)
  • SSH key-only auth, no root login
  • fail2ban with custom jails
  • IPv6 hardening (if not used)
  • Private VLAN for back-end traffic
  • BGP / OSPF as needed
  • DNS over HTTPS for outbound
24

Security baseline

  • CIS Level 1 profile applied
  • AppArmor / SELinux enforcing
  • Auditd with CIS rule set
  • AIDE file integrity monitoring
  • rkhunter + chkrootkit scheduled
  • ClamAV on mail and uploads
  • Unattended security updates
  • Strong password policy (pwquality)
22

Web stack

  • Web server tuned (worker pools, event loops)
  • PHP-FPM with opcache + JIT
  • HTTP/2 + HTTP/3 enabled
  • TLS 1.2+ only, strong ciphers
  • Security headers (HSTS, CSP, X-Frame)
  • ModSecurity + OWASP CRS
  • Rate limiting per IP and per route
  • Gzip / brotli compression
18

Database

  • MySQL/PG hardened (no remote root)
  • Buffer pool sized for RAM
  • Slow query log enabled
  • Connection pool (ProxySQL or pgBouncer)
  • Daily logical backup + weekly physical
  • Backups encrypted + offsite
  • Indexes reviewed, FKs verified
  • Binlog / WAL archive enabled
26

Monitoring + ops

  • Prometheus node_exporter + custom metrics
  • Centralized log shipping (Loki or ELK)
  • Alert routing (PagerDuty/Opsgenie)
  • Uptime checks (12 global PoPs)
  • Capacity dashboards
  • Runbook repo with 30+ scenarios
  • On-call rotation + escalation
  • Backup verification (monthly restore test)
Pick your stack

Pre-built stacks for common workloads.

LEMP

Linux + Nginx + MySQL + PHP
  • Best for: WordPress, Laravel, custom PHP apps
  • Tuned: php-fpm 5-10 child workers, opcache 256MB
  • Cache: Redis object cache, Nginx FastCGI cache
  • Bonus: WP-CLI pre-installed

LAMP

Linux + Apache + MySQL + PHP
  • Best for: legacy PHP apps, .htaccess-heavy sites
  • Tuned: mpm_event, mod_php disabled (use FPM)
  • Cache: Varnish or Memcached
  • Bonus: mod_security WAF enabled

OLS / LiteSpeed

OpenLiteSpeed + MariaDB + PHP
  • Best for: high-traffic WordPress, Magento, WooCommerce
  • Tuned: event-driven, ESI, LSCache
  • Cache: LiteSpeed Cache (drop-in for WP)
  • Bonus: QUIC + HTTP/3 out of the box

Node + NGINX

Node.js 20 LTS + PM2 + NGINX
  • Best for: Next.js, Express, custom Node apps
  • Tuned: PM2 cluster mode, 0-downtime reload
  • Cache: NGINX microcache, Redis
  • Bonus: yarn + pnpm + npm configured

Python + Gunicorn

Python 3.12 + Gunicorn + NGINX
  • Best for: Django, Flask, FastAPI
  • Tuned: gunicorn workers (2 * CPU + 1)
  • Cache: Redis, Memcached
  • Bonus: pyenv, poetry, pipenv available

Java + Tomcat

OpenJDK 21 + Tomcat 10 + NGINX
  • Best for: Spring Boot, Java EE apps
  • Tuned: G1GC, JVM heap sized to RAM
  • Cache: NGINX + Redis
  • Bonus: Maven, Gradle pre-installed
Why use us

The math behind 4-hour server setup.

DIY (in-house engineer)
40 hours
Hire a freelancer
18 hours + $1,200
Big 4 consulting firm
24 hours + $8,500
Our team
4 hours + $299

And every setup is reproducible: we have runbooks, scripts, and Ansible playbooks for every step. Next server, faster.

Customer stories

What teams say about our setup service.

"We had a new client that needed 12 production servers configured for Black Friday, with 2 weeks notice. The team provisioned all 12 in 5 business days, each with custom LEMP + Redis + Memcached + 30+ hardening rules. We made Black Friday with days to spare."
Vikram Shah
CTO, FinServe Solutions
"I was a Linux novice. They set up a 4-server cluster for my SaaS in 6 hours, walked me through every setting, and left me with a 30-page PDF I still reference. Best money I have ever spent on infrastructure."
Sarah Chen
Founder, NexaAI
"Our in-house engineer left. We had 8 production servers with no one to run them. The setup team onboarded, documented everything, and now we are a managed customer. The transition was seamless."
Michael Torres
CISO, FinServ Global

A new server, ready in 4 hours.

150-point checklist. Hardened baseline. 30 days of free support.
Get Setup See Checklist