Anycast-routed traffic is inspected at our network edge by 1.5 Tbps of DDoS scrubbing capacity. Volumetric attacks (SYN flood, UDP flood, amplification) are absorbed before they reach your server. Always on, no opt-in.
2. Web Application Firewall (WAF)
ModSecurity-powered WAF with the OWASP Core Rule Set (CRS) pre-loaded. Protects against SQL injection, XSS, RCE, LFI, and 300+ other web attacks. Per-customer rule allowlisting available.
3. Malware Scanner & Cleanup
Daily deep scans of every file on your account using ClamAV, ImunifyAV, and our own custom signatures. Infected files are auto-quarantined, and you can roll back to a clean backup in one click.
4. Encryption Everywhere
Free auto-renewing Let's Encrypt SSL on every domain and subdomain. TLS 1.3 enforced. AES-256 encryption at rest on all storage. Optional customer-managed keys (BYOK) on VPS and dedicated.
5. Daily Off-Site Backups
Automated daily backups retained for 30 days, stored on separate infrastructure in a separate datacenter. 1-click restore from your control panel or via our support team. Included free on every plan.
6. Identity, MFA & Access Control
Mandatory TOTP-based 2FA for all accounts. IP whitelisting and SSH key enforcement on VPS and dedicated. Role-based access control (RBAC) for teams. SSO (SAML/OIDC) on enterprise plans.
24×7 Security Operations Center
A team of humans, not just SIEM alerts.
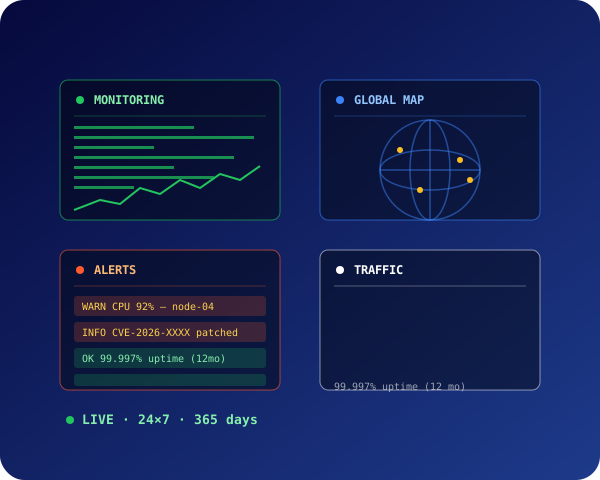
Our SOC monitors every customer server 24 hours a day, 7 days a week, 365 days a year. We do not just collect logs "” we have trained incident responders on shift who triage, contain, and remediate in real time.
@lang('24×7×365 monitoring "” @lang('three shifts covering IST, GMT, and US/Pacific time zones.')
@lang('<5 min CVE patching "” @lang('critical CVEs are patched across the entire fleet within 5 minutes of public disclosure.')
@lang('SIEM + UEBA "” @lang('security information & event management with user-and-entity behaviour analytics.')
@lang('Yes. We pay between ₹5,000 and ₹5,00,000 for valid security findings, depending on severity. Report to security@bizhostwiz.com.')
@lang('Yes. All backups are encrypted at rest with AES-256 and in transit with TLS 1.3.')
@lang('Yes. You can upload your own commercial SSL certificate (from DigiCert, Sectigo, GoDaddy, etc.) via your control panel, or use our free auto-renewing Let\'s Encrypt certificates.')
@lang('Critical CVEs are patched across the entire fleet within 5 minutes of public disclosure. High severity within 24 hours. Medium and low are batched into weekly maintenance windows.')
@lang('Found a Security Issue?')
@lang('Responsible disclosure program with paid bounties.')
@lang('If you find a valid security vulnerability in our infrastructure, we will reward you and publicly credit you (if you want). Send details to security@bizhostwiz.com with a PGP-encrypted proof-of-concept.')